
 KOR
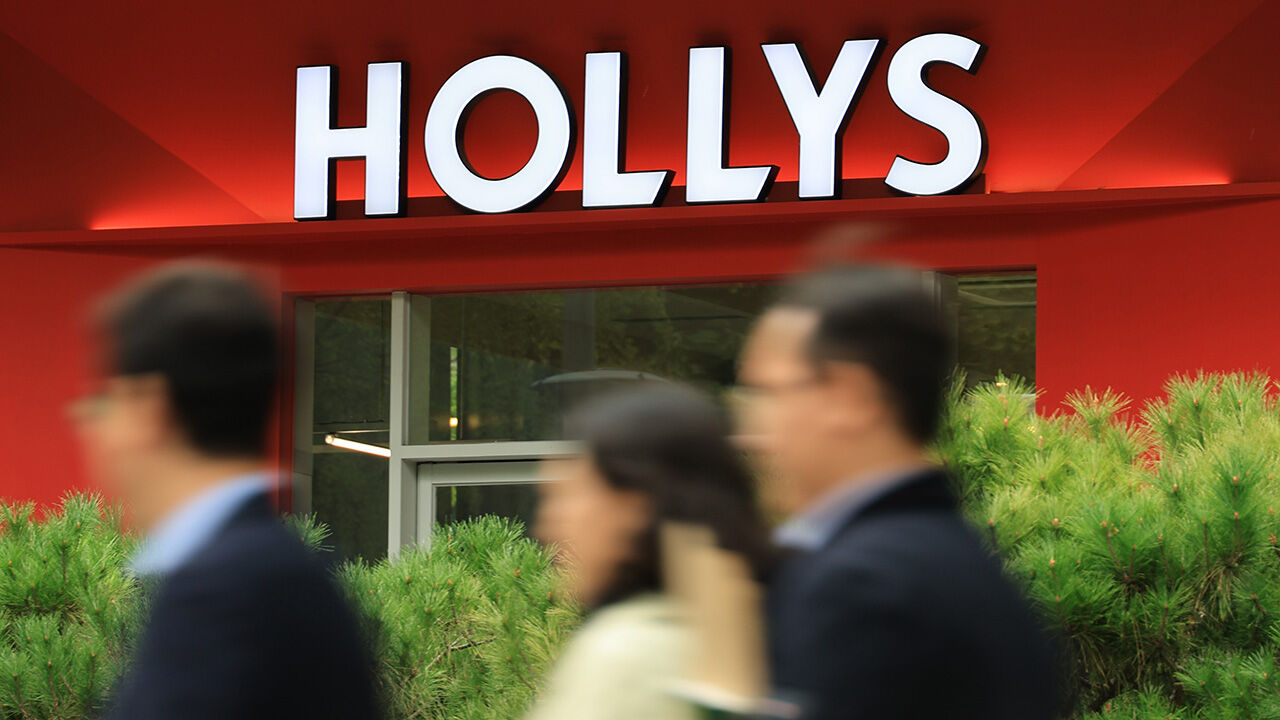
▲ Citizens walk past a HOLLYS store in Seoul.
Customer personal information has been leaked following a hacking incident targeting the membership system of coffee chain HOLLYS.
According to the coffee industry, HOLLYS confirmed on October 16 that unauthorized external access to its membership system led to a data breach, and posted a notice regarding the incident on its official website at around 9:36 p.m. that same day.
HOLLYS urged customers to immediately change their membership account passwords, and also requested that users change passwords for any other services using the same ID and password combinations.
The company further emphasized that customers should not respond to or click on links in phone calls, text messages, or emails from unknown sources.
Emphasizing that HOLLYS never sends links via text message or asks for passwords, financial information, or payment details, the company added, "We deeply apologize for causing concern to our customers due to this incident," and stated, "We will do our utmost to protect customer information and minimize damage."
The customers whose information was leaked are those who signed up for HOLLYS membership before February 11, 2020.
However, specific details—such as the exact number of affected customers and whether the leaked information has been exploited externally—have not been disclosed in the notice.
The leaked items include IDs, passwords, names, dates of birth, phone numbers, addresses, email addresses, and duplicate registration verification information.
Amid a recent series of personal information leak incidents at corporations, consumer anxiety is expected to grow now that customer data has leaked from a coffee chain used in daily life.
Yesterday, the HOLLYS mobile and PC websites experienced service disruptions, becoming temporarily inaccessible for a while.
HOLLYS estimated that the personal information leakage occurred due to external hacking between September 3 and October 7.
HOLLYS stated that it has blocked the unauthorized access paths, implemented stronger authentication measures, and stepped up monitoring for abnormal login attempts.
The company also reported that it has notified relevant authorities and is cooperating with their investigations.
However, it was revealed that even today, four days after recognizing the incident, HOLLYS has yet to properly ascertain the scale of the damage.
An official from the KG Group, to which HOLLYS operator KG F&B belongs, stated only that the scale of the damage is currently being assessed as of today.
In particular, it was found that after recognizing the accident on October 16, HOLLYS posted the relevant information only on its website, and notified customers via text message two days later, yesterday.
One whistleblower, who stated that they had previously joined and then withdrawn from the HOLLYS membership, said they received a text message from HOLLYS regarding the data leak yesterday, raising suspicions that the breach occurred because HOLLYS failed to delete and continued to retain the registration information of withdrawn members.
The whistleblower also expressed frustration, stating that when they called the HOLLYS customer center listed in the text message to check the details, the automated response system guidance repeated endlessly with no way to speak directly to a representative.
Previously, in September 2020, the KG Group acquired a 93.8% stake in Hollys F&B for 145 billion won.
The operator subsequently changed its name to KG Hollys F&B and then to KG F&B in 2024.
(Photo: Yonhap News)
※ Please note: This article was translated by AI and may contain errors.

 Video News

 Video News
 Video News
 Video News