
 KOR
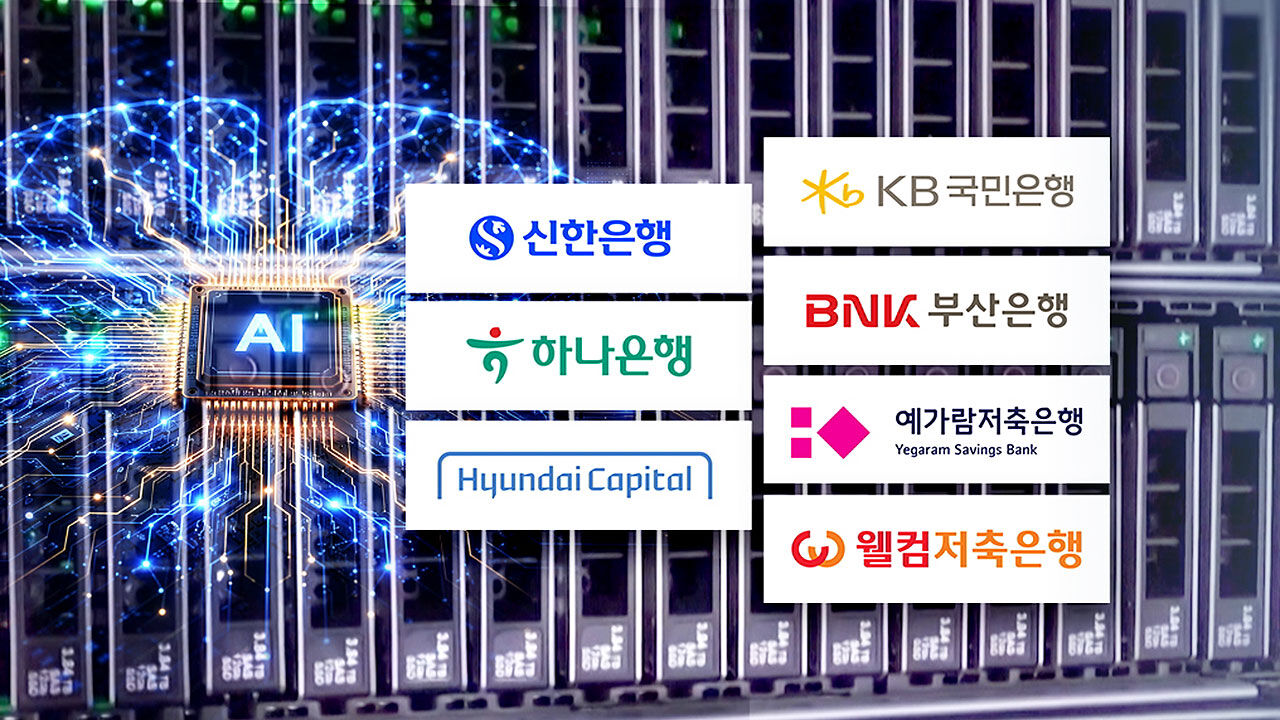
Clues regarding the identity of the person suspected to be behind recent hacking attacks targeting South Korea's financial sector have been captured for the first time.
In an analytical report released on October 7 (local time), global cybersecurity firm CrowdStrike stated that the attacker is likely a 26-year-old individual residing in Guangdong Province, China.
However, the firm drew a line, noting that this is a circumstantial estimation and not a definitive identification.
According to CrowdStrike, the clues were exposed while the attacker was using the generative artificial intelligence (AI) coding tool "Claude Code."
The attacker asked Claude to write a security researcher resume containing the results of their penetration testing, and personal information including their initials, Telegram account, educational background, and place of residence was entered in the process.
The report stated that the same Telegram account was discovered in connection with other cyberattack circumstances as well.
It was found that the same account name was used in a session investigating vulnerabilities in a Telegram-based non-fungible token (NFT) futures marketplace and in circumstances targeting a payment platform in China.
Based on these cross-circumstances, CrowdStrike suggested the possibility that it is the same individual, while adding that the identity cannot be concluded with certainty based solely on the information secured so far.
Previously, CrowdStrike analyzed that attacks targeting South Korean financial institutions took place between the end of last month and early this month, and that the attacker utilized "ARTEX," an open-source agentic penetration testing tool developed in China, along with a large language model (LLM).
The attacker, presumed to be a Chinese speaker, was assessed with medium confidence to likely have been motivated by financial incentives.
※ Please note: This article was translated by AI and may contain errors.
Suspected Hacker Behind South Korean Financial Sector Cyberattacks Estimated to Be 26-Year-Old in China's Guangdong Province: Clues Discovered

Copyright Ⓒ SBS & SBSi. All rights reserved.
Copying, redistribution, and unauthorized use in AI training are strictly prohibited.
Copying, redistribution, and unauthorized use in AI training are strictly prohibited.
Trending Now
-
 Video News
Café Students Criticized for Throwing Banknotes at Worker and Laughing
-
Video News
"Sorry for the Baby's Crying" Days Later... Why a New Mother Was Touched
-
Video News
Using Phone in the Dark Before Bed: Warning of Sudden Blindness Risk If Ignored
-
Video News
Appearing at Night to Warn, "Don't Do That"... "Bukang-i Vigilantes" Emerge
-
Video News
"Bang"... Live Rounds Fired in the End: The Dangerous End of a Reckless Rampage
 Video News
 Video News
 Video News
 Video News
 Video News