
 KOR
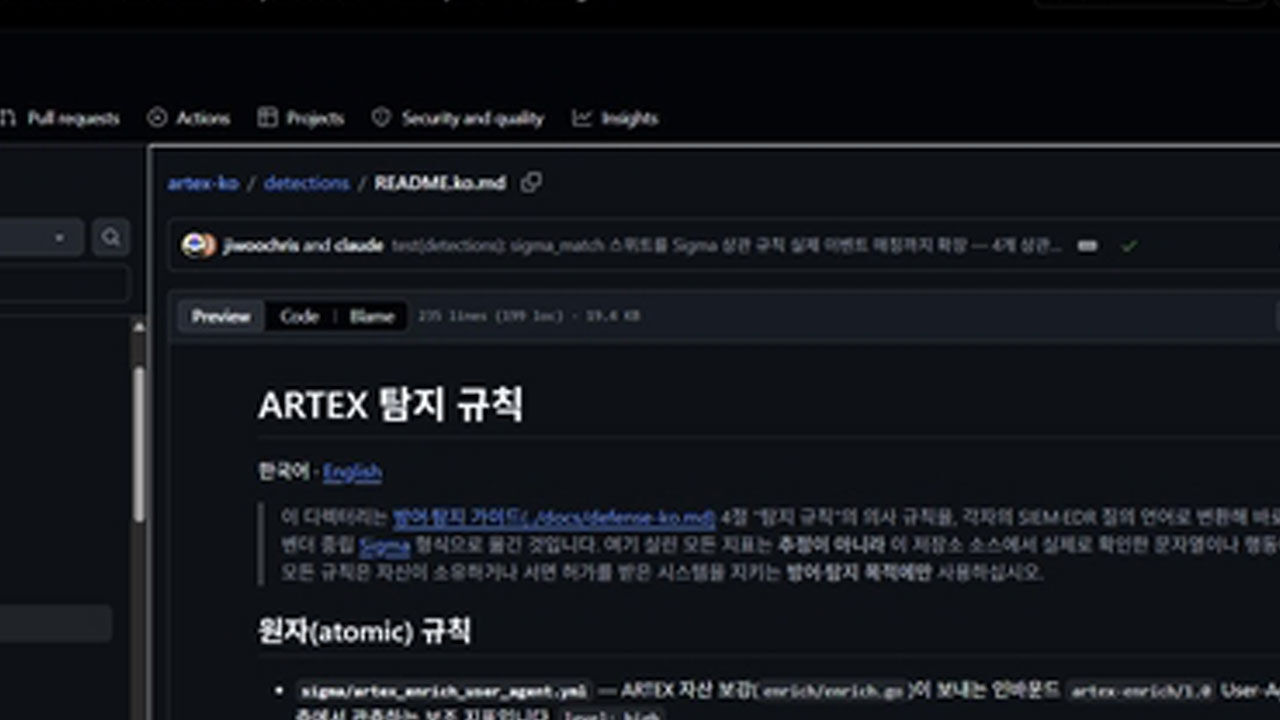
▲ Korean-language edition of ARTEX
ARTEX, a Chinese-made artificial intelligence (AI) penetration testing tool recently reported to have been utilized in a series of hacking attacks targeting South Korea's financial sector, is halting its public development following controversies over its abuse.
The developer of ARTEX stated that, citing the tool's misuse in cyberattacks, updates will be halted and no additional versions will be released.
Related pages have also reportedly disappeared from the developer platform GitHub.
However, as programs already distributed cannot be recalled, it is expected to be difficult to block cyberattacks utilizing ARTEX through the development halt alone.
According to foreign media outlets such as AFP and Reuters on the 10th, the ARTEX developer known as "Autumn-27" stated in a post uploaded to GitHub on the 8th that ARTEX had been abused, saying, "Considering the misuse of the tool, ARTEX will no longer be updated and will transition to a closed-source model."
The developer added, "Additional versions will not be made public to the public, and maintenance support will not be provided."
While ARTEX stated that using the tool for cyberattacks runs counter to the developer's intentions, it did not directly mention the hacking incidents that occurred in South Korea.
In addition, ARTEX claimed that it bears no responsibility for actions violating laws and regulations using the tool.
Reuters reported that the GitHub page for ARTEX has disappeared.
Experts pointed out that if ARTEX transitions to closed-source, it may become more difficult for new users to generate code.
However, a Chinese IT expert told AFP that this decision by ARTEX cannot remove already downloaded copies or prevent users from continuing to use them.
ARTEX is an autonomous penetration testing program designed to connect large language models (LLMs) so that AI agents can analyze attack targets, plan penetration routes, and execute security tools.
U.S. security firm CrowdStrike analyzed that attacks targeting South Korean financial institutions took place between late last month and early this month, and that the attackers utilized ARTEX alongside LLMs.
(Photo: Capture from GitHub, Yonhap News)
※ Please note: This article was translated by AI and may contain errors.



 Video News
 Video News
 Video News