
 KOR
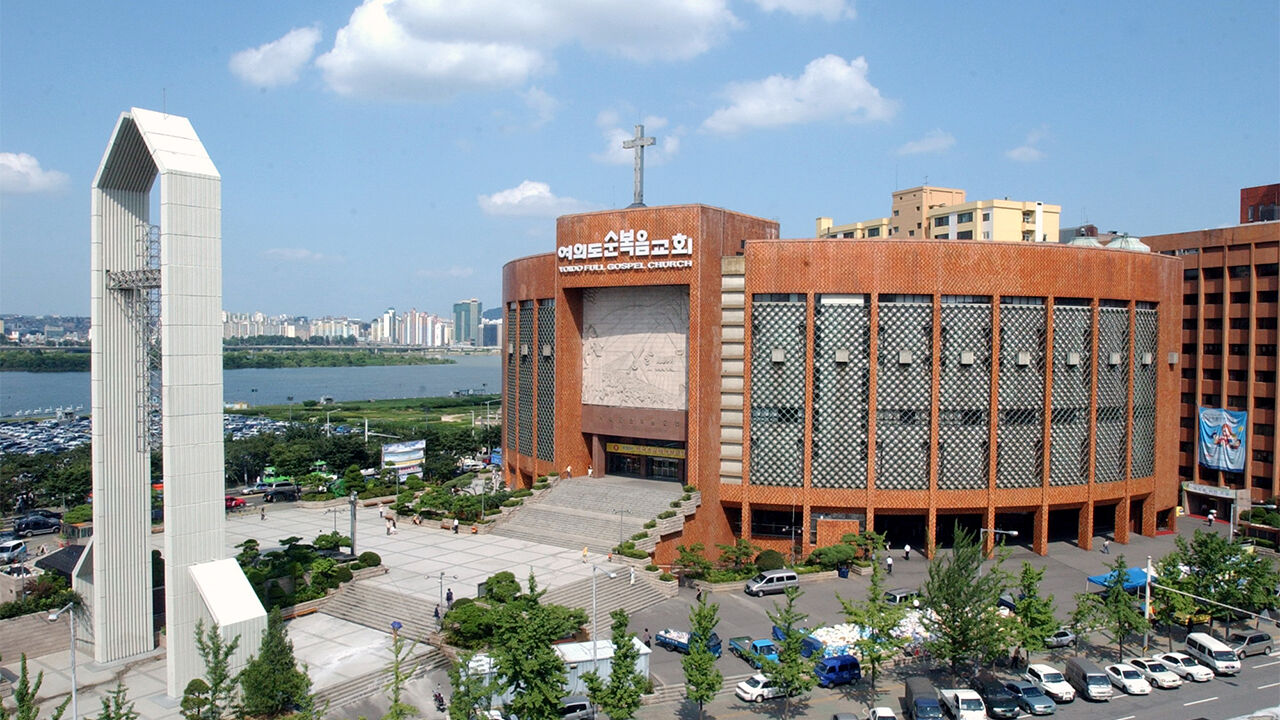
▲ A view of Yoido Full Gospel Church
Yoido Full Gospel Church, South Korea's largest church where signs of a cyberattack were detected, announced today (October 7) that its internal analysis suggests personal information, including the names and dates of birth of 850,000 church members, may have been leaked.
In a press release issued today, Yoido Full Gospel Church stated, "Immediately after being notified by the Korea Internet & Security Agency (KISA) at 3:00 p.m. yesterday of a suspected security breach in the church's information system, we launched an emergency security check and analyzed suspected leak data and system access logs with an external security specialist organization."
The church explained, "Among the seven sets of data suspected of being leaked, six sets—including records of parish transfers, title appointments, and baptism histories—did not contain personal information. However, we confirmed that one set concerning member information change histories contained some personal data."
The member information change histories contain the names, dates of birth, and change details of a total of 850,000 individuals, the church said, adding that this includes 2,629 records of resident registration number changes, 3,964 records of phone number changes, and 7,202 records of address changes.
It added that past donation records among the leaked materials contained voucher numbers, amounts, and details, but did not include personal information such as names.
Yoido Full Gospel Church stated, "We are in the process of notifying the affected members of the leak in accordance with relevant laws and procedures," and added, "Additional response measures were implemented at 1:00 a.m. today, including blocking external access and changing server passwords."
In addition, the church plans to replace existing firewalls to keep them up to date and conduct system vulnerability analysis and further security reinforcement work alongside specialized security firms.
Regarding the incident, Senior Pastor Lee Younghoon said, "The responsibility to safely manage and protect the precious personal information of our church members lies with the church," adding, "As the senior pastor, I feel a heavy sense of responsibility and sincerely apologize for causing concern to our members due to this incident."
He further stated, "We are taking this matter very seriously," and added, "While actively cooperating with the investigation and verification procedures of relevant authorities, we will take all necessary measures, including thoroughly reinforcing our information protection system to ensure that such an incident never happens again."
Previously, cybersecurity firm Oasis Security stated that it had identified large-scale member information from two large Korean churches on an overseas attacker's server.
(Photo provided by Yoido Full Gospel Church, Yonhap News)
※ Please note: This article was translated by AI and may contain errors.

 Video News

 Video News

